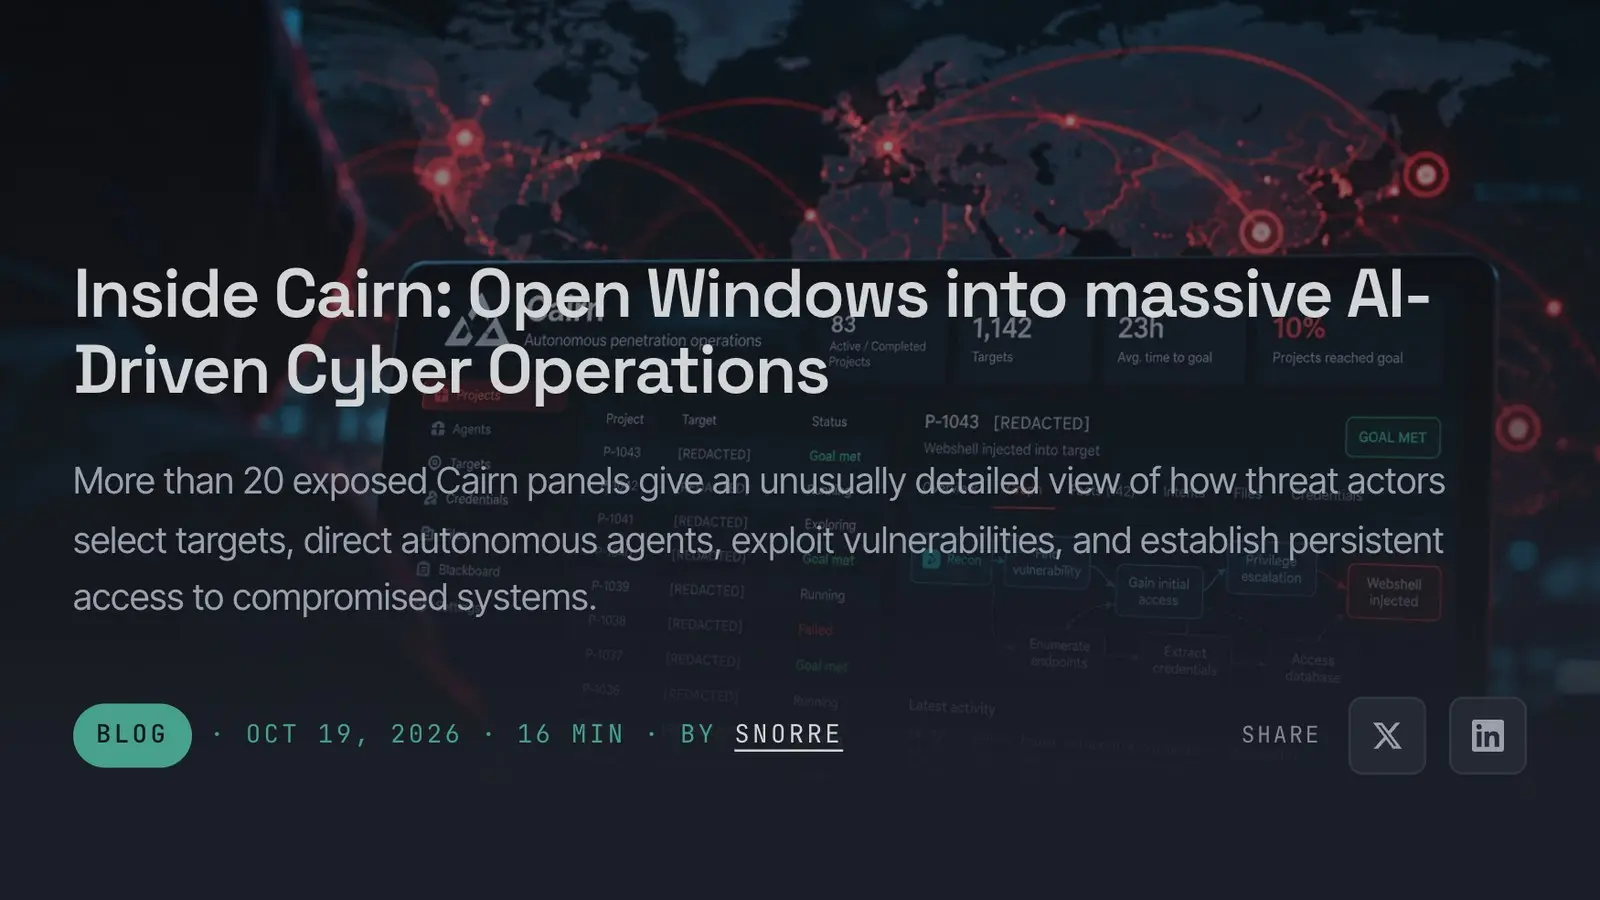
A Reuters investigation reports, citing NorForge researcher Snorre Fagerland, that one hacker used AI agents to get into more than 100 websites, mainly online stores in the US, Canada, Australia and Japan. Fagerland estimates the cost at roughly $50 per break-in. The researchers' report today describes the open-source tool.
What the researchers found
The researchers say they found more than 20 control panels for an open-source agent platform called Cairn left exposed online. The panels show attackers picking targets, hunting for weaknesses, breaking in and keeping access, with AI agents doing the work end to end.
Some exposed panels appear to belong to legitimate red teams, the security firms paid to test their clients' defenses. The researchers say leaving those open puts those clients at risk. Cairn's author said in a post on X that the platform "was not designed for hacking attacks," the news agency reports. The author did not answer its questions.
The numbers
The campaign began Sept. 25, per Fagerland, as the news agency reports. By late last week the agents had tried more than 1,200 sites. Per the same reporting, the hacker's instructions ran under 100 Chinese characters.
Successful break-ins typically took about 23 hours. Fagerland estimated the campaign, which appeared to use a mix of DeepSeek and Claude Code, consumed roughly $5,000 of tokens, about $50 per successful hack. That is his estimate, not the hacker's.
Who was named
The researchers' report did not name the victims. The news agency identified Deere, SharkNinja and Cummins by reviewing the hacker's Cairn activity, and each gave a statement:
- Deere took "necessary remediation actions" and has "no indication that sensitive information was accessed."
- SharkNinja says only a standalone product-support site was affected, and that it is contained.
- Cummins says it is investigating a possible attack on a site run by a third-party vendor.
The news agency could not determine how much data, if any, was extracted in this campaign. Two smaller businesses also acknowledged being compromised.
What shoppers can do
Because the investigation could not establish whether data was taken, these are standing precautions, not a response to a confirmed leak.
- Treat unexpected messages about an order, a refund or a product registration with caution, and go to the retailer's site yourself instead of tapping the link.
- Pay with a virtual card where your bank offers one, so a leaked number is easy to cancel.
- Use passkeys where a site supports them. Google's scam protections for Android cover what your phone can flag.
Why it matters
Fagerland told the news agency he had assumed hacker agents would need at least some human supervision, and that it was now obvious the technology had moved past that. The trade-off is in the tooling: Cairn's author says it was built for multi-agent work, not attacks, yet the same open platform runs both.
That puts the weight on defenders and site owners, since one person can now direct a long campaign with a short instruction. It also fits a wider pattern of agent fleets pointed at the open web. Separately, some services are shutting agents out.